Real threat intelligence.
Now, for free.
The free Community Tier is open, so any analyst can put AI-powered threat intelligence to work with no budget and no team. Create your account and you are in: the dashboard is already populated from open sources by the time you log in for the first time.
No credit card, no catch.
Pick your path.
Liberty91 works for individual analysts, for MSSPs delivering to many customers, and for security leaders who want threat intelligence working for them without building a team to do it. Pick whichever fits you.
Start for free.
Individual analysts and small teams can put AI-powered threat intelligence to work on the free Community Tier, no credit card needed. Create your account and you are in.
Start for Free→Deliver it to your customers.
Run a white-label threat intelligence service across your whole customer base, under your own brand, priced per customer. See how the MSSP model works, or talk to us about partnering.
Explore white-label→A CTI function, without building one.
Get what a mature threat intelligence team would produce, tied to your own assets and suppliers, without having to build that team first. The quickest way to see it on your own organisation is a short demo.
Book a demo→What the Community Tier gives you.
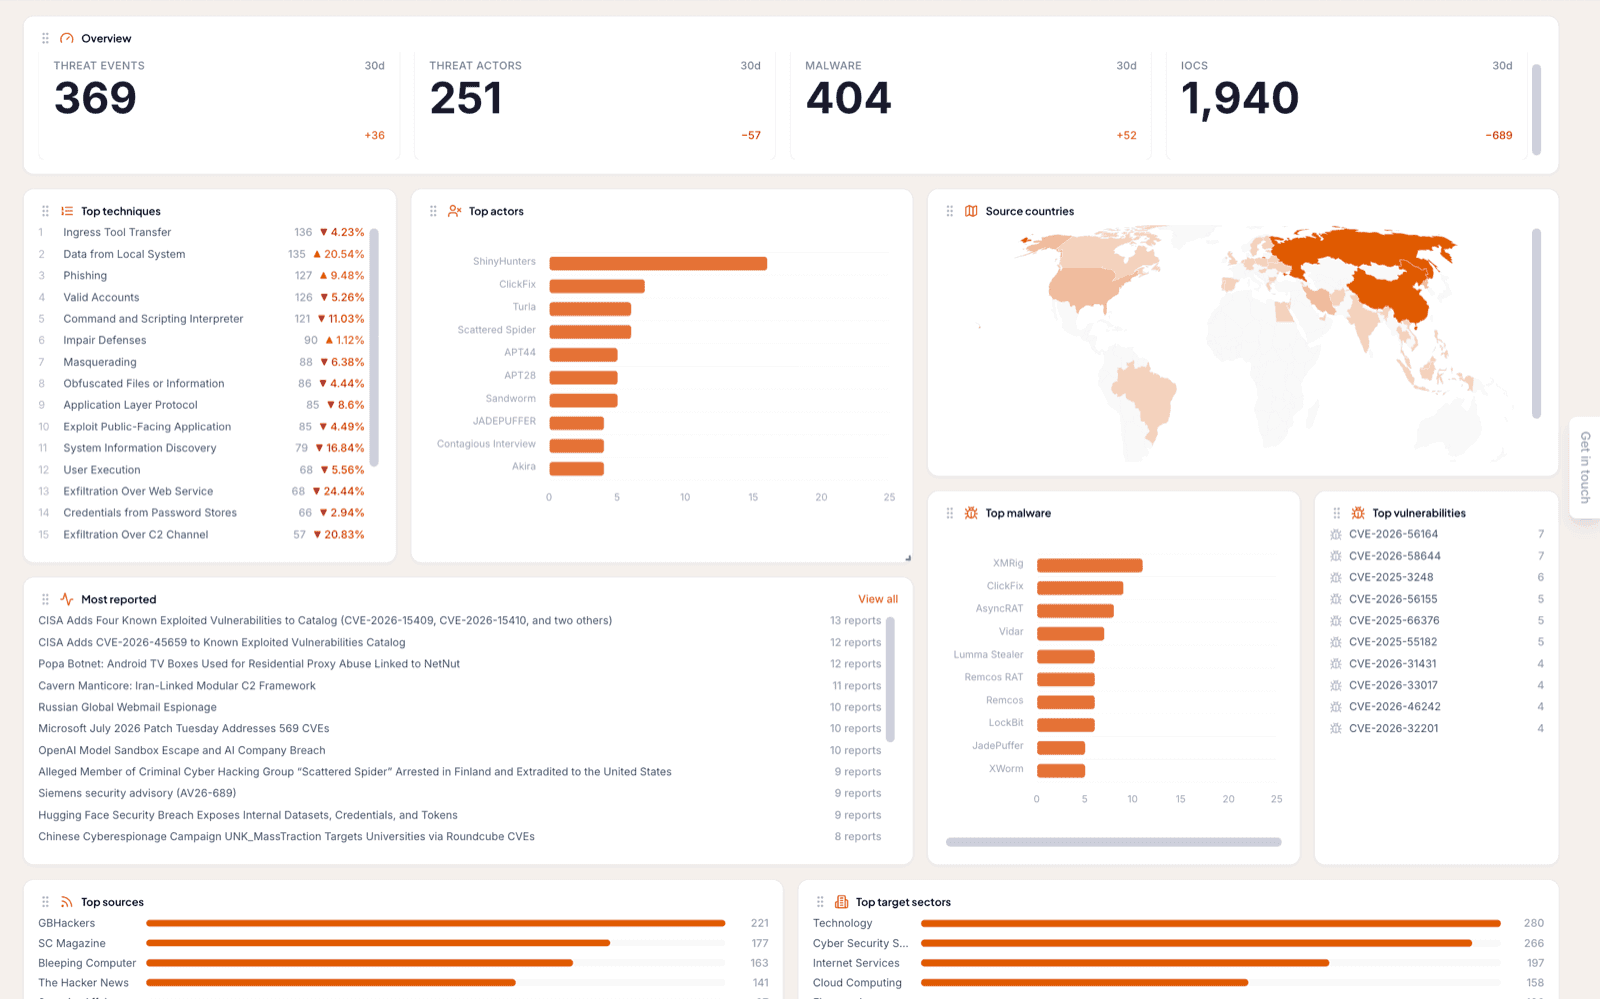
Real, tailored intelligence you can use from day one: one organisation, curated open sources, a week of history and two Intelligence Packages a month. The full plan comparison is on the pricing page.
Curated sources, one platform
Open-source feeds we have already picked out come into one place. Every incoming event is collected and worked through for you, then checked against your own threat library, so nothing relevant slips past and you are not stitching feeds together by hand.
Every event, enriched
You get more than a daily report. Every event is worked through as it arrives: indicators of compromise (the IP addresses, domains, and file hashes tied to an attack) pulled out, given context from other sources, and scored; the attacker behaviour matched to MITRE ATT&CK; and the actors, malware, and tools involved identified, all written up so you can read it and act on it.
Yours to take further
Use it alongside our free, open-source CTI Skills for your AI coding agent, and move up to a paid tier for STIX bundles, API access, and more sources whenever your needs grow.
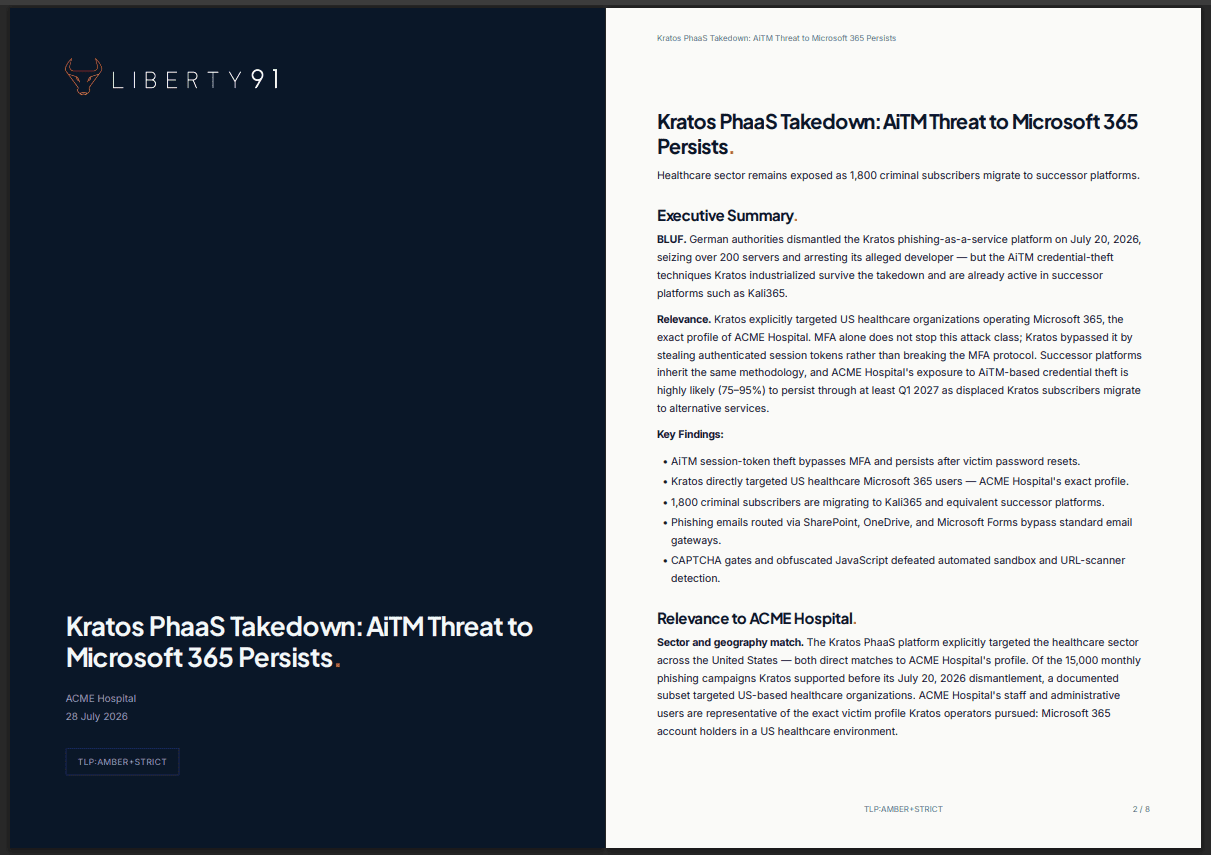
A finished report written for one organisation, with indicators of compromise and detection rules, drafted in real time and ready to act on.
Want to build it yourself instead? Our open-source CTI Skills pack is free and MIT-licensed today.
Create your account.
It takes a minute and needs no credit card. Your first session is mostly reading, because the agents have already collected and worked through the recent reporting before you arrive. When you hit a wall you care about, the pricing page shows what each paid tier adds.
Start for Free →